Showing posts with label what. Show all posts

Friday, October 15, 2021

What You Might Want To Know About Vpn Fortigate And Why

Now you can select how you want your internet traffic to use the VPN services. If its always on you can be sure that your internet traffic wont be sent if the VPN goes down.
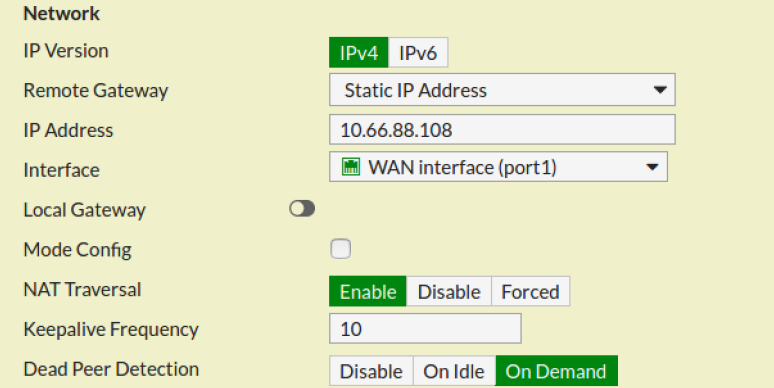

Ipsec Vpn Configuration Guide For Fortigate 60d Firewall Zscaler

You want to delete an unused AddressObject but you.
What you might want to know about vpn fortigate and why. So you want to set the NAT-T keepalives. The most important part in our scenario is the fact that communication is based on certificates so its independent on user accounts and their password. I recently rebuilt all my tunnel SSID to bridge with vlans and its night and day 421-E on a 60D Edit.

Though I generate and archive syslogs from the FortiGates and my other devices they are not nearly as useful as the logs on the FortiAnalyzer especially as Fortinet has some non-standard fields or at least they used to -- havent checked in a while. Anything sourced from the FortiGate going over the VPN will use this IP address. Not exactly Merakis fault but if Meraki didnt rely on MS for VPN connectivity software the issue would be null.

Fnsysctl ifconfig -a port1. If you need high throughput Fortinet will be the best. I want to add SSL VPN in the future but for now PPTP is fine.

In ExpressVPN Network Lock is the Kill Switch. If youre considering a VPN you might want to read these articles first. Lets look at some more diag vpn outputs.

Bridge is performant but can involve using vlans unless you want all your SSID in the same subnet as the AP. You will need to create those rules in order for the VPN to function properly. Nat_traversalyes Also DPD could be used within your setup.

Its not at all uncommon to see 100-1k vpn-ipsec-tunnels nailed to a fortigate. From a sheer performance aspect bridge is the way to go. Although the differences in number between them is still debatable.

A few notes on the FortiGate VPN configuration. If you concern more to applications latency Palo Alto is the right answer. Fortigate has a CLI interface for advanced users that want that level of control.

I havent done a VPN client solution with Fortigate to compare. The above does not include the firewall rules ACLs that would be required to allow inbound VPN traffic to reach your network or outbound VPN traffic to reach the internet. Port1 is the port I needed to get the info for you can change this accordingly.

At the moment I got a working configuration but some things are not working properly. If your in AWS you probably want NAT-T so that might be part of the problems with e UDP sessions dying. I often hear that only US connections would be accessing their services so why allow others who might not be on the up and up.

One of the most important option within fortigate diagnostics is our phase1 filters. Understand you wanted performance aside but. CLI My_Forti_OS get system performance firewall statistics There is also a more generic system performance command that will not only give you some valuable system-wide network and session information but it will also show some cpu data and general stats for IPSVirus-detection services that.

Check out the screenshot below. This object dependency you are likely to find in a default configuration for a FortiGate 60B and other products that use Switch to Interface Mode. In a hub or a service provider arena you might havd a dozen or more vpn-tunnels.

Everything is working fine but Ive got some problems with the PPTP VPN connection. If you need more up to date or get as quick as possible for zero day attack you could choose Check Point. Dpddelay30 dpdtimeout60 dpdactionrestart Just match it to the fortigate if you.

The Fortigate has a stat specific for anything that goes though its fw service and that is. Also you should keep in mind that a VPN service that offers a dedicated IP address is generally much more expensive and less secure for your privacy since its easier to associate search queries with your address. On some FortiGate units such as the FortiGate 94D you cannot ping over the IPsec tunnel without first setting a source-IP.

To prevent leaks employ a Kill Switch when using a VPN. Sincere about security and privacy StrongVPN Review. As you know for communication between FortiGate and FortiManager responsible is FGFM protocol which is well described in the FortiGate FortiManager - Communications Protocol Guide.

Why you might need to change it. In this scenario you must assign an IP address to the virtual IPsec VPN interface. Of course thats not 100 guaranteed and you still might be asked to fill in a CAPTCHA if you are using a VPN anyway.

Run an Ifconfig from the Fortinet FortiGate by running this command. Ive got a fortigate 40C here and copied the config mainly from a Fortigate60. So you might want to try it out to see if it works for you.

The issues seem to be caused by Microsoft updates affected the VPN in Windows 10.

Thursday, July 29, 2021

What You Dont Find Out About Fortigate Ssl Vpn

For some reason when you view references from VPN IP Sec IKE it doesn t always show all references at least in 50x. Enter the details for your connection.


Fortinet Youtube Access Control List Connection Access Control

Dont want to leave you hanging.

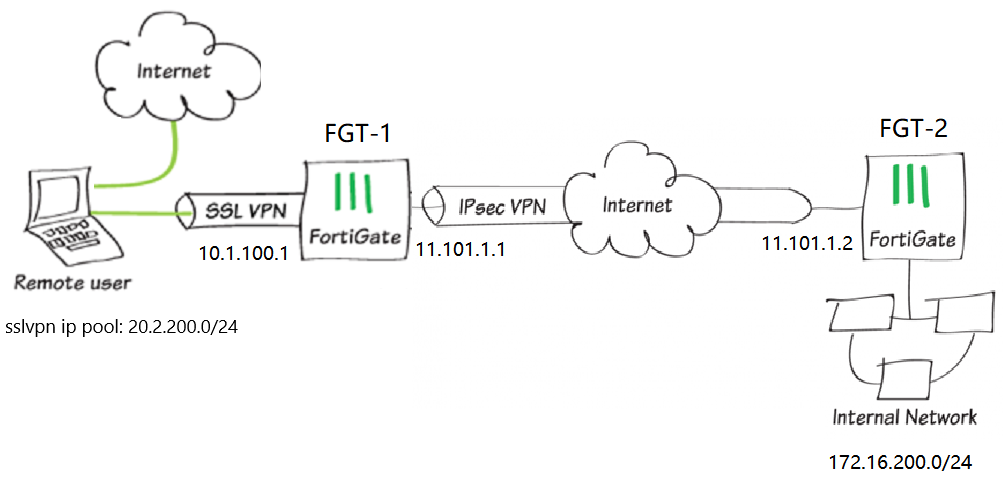
What you dont find out about fortigate ssl vpn. I dont have a console cable so thats my next step - wire the console into a client and take a look when things go awry next. The only solution I have to this right now is a reboot either via a physical power cycle or accessing the administrative interface via SSL-VPN for a CLIGUI reboot. Since it seems to be a client to network VPN if switching to SSL is an option on Windows 10 in the Microsoft Store there is a free official Forticlient SSL VPN Win10 app that simply add an option into Windows VPN.

500 a month Get VPN Access. I dont think you care what the sources and destinations are. The IP address of your second Fortinet FortiGate SSL VPN if you have one.

We will be using OPENSSL to generate the CA and certificates. For information about how to interpret log messages see the FortiGate Log Message Reference. This is a pretty straightforward step and were sure you dont need.

After setting up a SSL VPN tunnel one of the biggest complaints I get is I cannot get to my shares. FortiGate firewalls are the next generation of firewalls by Fortinet one of the leading names in the cybersecurity industry. Make a note of the example below specifically the Common Name Identifier.

This is a detailed guide on how to configure a SSL VPN with certificate authentication on a Fortigate. Logging VPN events. FortiGate 300D - Allow Fortigate SSL VPN To 2nd WAN Interface.

Generate the CA or root certificate Certificate Authority You will need to generate a root certificate to sign the Server and Client certificate. Within cli you have many options under the ssl vpn config. Go back to FortiGate and navigate to the VPN section.

I took a quick peak and couldnt find the option to disable it and Fortigates arent my specialty. Save and Restart FortiGate. The guide will talk you.

On the ForiGate navigate to Users Devices LDAP Servers and click Create New. Fortigate Ping and Traceroute options. You can specify secrets for additional devices as radius_secret_3 radius_secret_4 etc.

You can configure the FortiGate unit to log VPN events. This will be the user that would to access the SSL VPN. Pushing DNS Suffix to Fortigate SSL VPN.

Also this example assumes your SSL VPN is already setup. As for IPsec it might be different depending on the FortiOS version but mine ask to specify if. To log VPN events.

For IPsec VPNs Phase 1 and Phase 2 authentication and encryption events are logged. I couldnt find a post with my scenario so Im asking for some help. VPN Comparison0Best Reviews2019-07-12 160840Compare the top 10 VPN providers of 2019 with this side-by-side VPN service comparison chart that gives you an overview of Ssl Vpn Fortigate all the main fe.

This is easy to remedy but seems to be in CLI only. Add a comment 1 Answer Active Oldest Votes. Look under the Connection Settings and find the Server Certificate.

FortiGate SSL VPN v54. Hi I have to look a Fortigate with firmware version 6011 later today and prevent users from connecting with their Forticlient VPN while instead the network. Add your authentication server.

Go to Policy Objects IPv4 Policy and select Create New. For example if you need to modify the source IP address for a ping or trace you have that option and many more. SSL VPN Troubleshooting debugging at the Fortigate CLI common ssl vpn problems.

If its not follow this post for help. We unfortunately do not currently have a support contract that includes in-depth technical support on the FortiClient side and Ive been through the channels on the FortiGate side on everything thats available for them to tell me. Below shows a quick run down of the 8 Key steps needed when creating a SSL VPN on a fortigate.

How many SSL-VPN users can I connect is there some limit of concurrent connections or special licen. Find the certificate you want to install in the drop-down menu. Go to Log Report Log Settings.

I find that the best way to discover references is by going to system network interfaces and enabling the references column. Thanks to the growing trend of working remotely as well as rising cyber-threats many are looking to secure their communication through SSL VPN. And do you know what you need for an SSL VPN.

You can specify additional devices as as radius_ip_3 radius_ip_4 etc. Within the Fortigate firewall you can modify many ping and traceroute options to suite what needs you might have. Mar 21 15 at 1432.

Im intend to deploy a Fortigate on GCP via Marketplace in the PAYG pay-as-you-go modeMy question is. 3 I finally found out the solution the logs are placed in the user appdata folder. Both ping and traceroute are crucial network troubleshooting tools.

Create a normal security policy from sslroot to wan1 to allow SSL VPN traffic to connect to the Internet. So you should just go to. Im looking for some help with getting our Fortinet SSL VPN using FortiClient into a stable and workable state.

The secrets shared with your second Fortinet FortiGate SSL VPN if using one. If traffic comes in via interface just go out the same interface. Create an SSL VPN security policy with SSL VPN user authentication to allow SSL VPN traffic to enter the FortiGate unit.

Common references include routes firewall objects firewall policies and phase-2 vpn objects. Under SSL select Settings. Create a Username and Password and select the Authentication method.

This is because the Domain suffix has not been pushed out to their tunnel interface. You can leave the gateway at 0000 and itll sort itself out.